Skip to product information
1 of 1

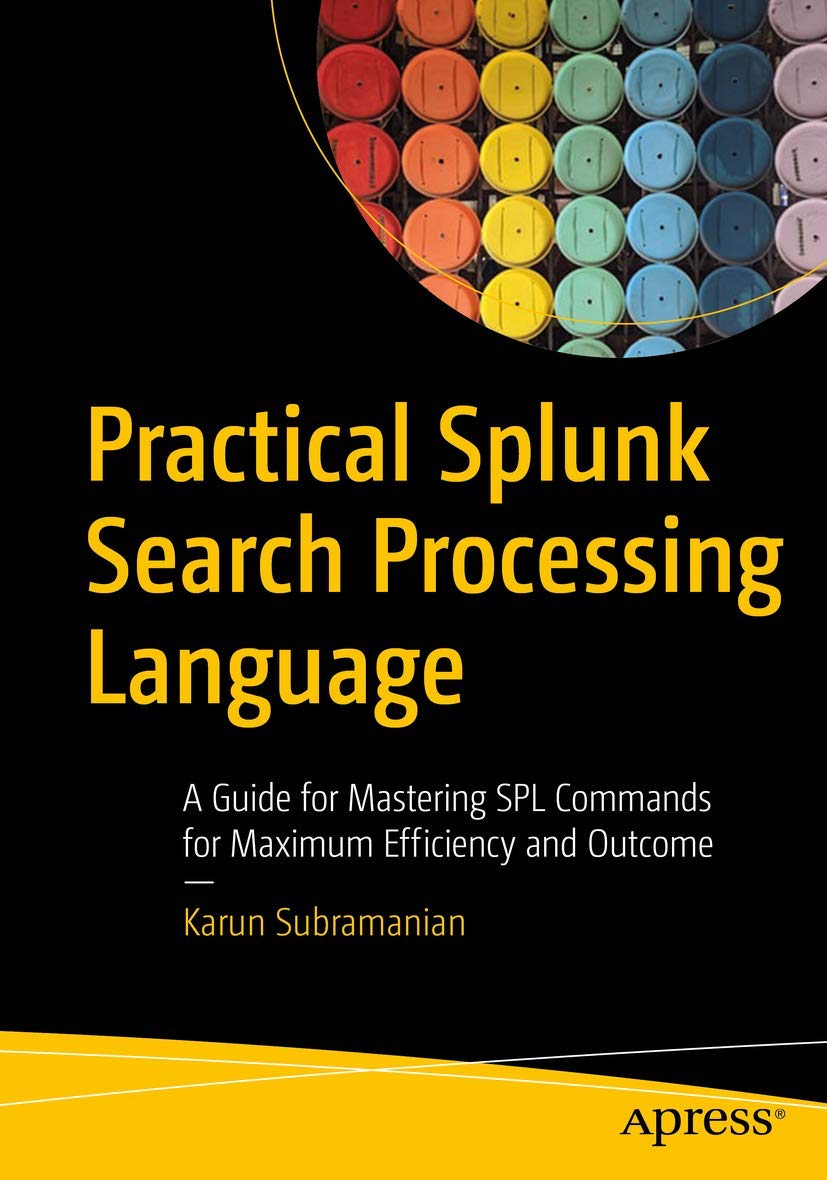
Stock cover image; actual copy may differ.

Practical Splunk Search Processing Language: A Guide for Mastering SPL Commands for Maximum Efficiency and Outcome

Regular price
$38.02 USD
Regular price
Sale price
$38.02 USD

Book details

Subramanian, Karun

Condition
Acceptable
Format
Paperback
ISBN
Not listed

This book is in acceptable condition and may have highlighting and or writing throughout. The actual cover image may not match the stock photo, dust jacket may be damaged or missing. Book may show internal and or external wear on spine or cover and may be slightly skewed or have creased pages. This is a used book so codes may be invalid or accompanying media may be missing. May be an Ex library book with stickers and stamps.

Shipping calculated at checkout.
Description
Use this practical guide to the Splunk operational data intelligence platform to search, visualize, and analyze petabyte-scale, unstructured machine data. Get to the heart of the platform and use the Search Processing Language (SPL) tool to query the platform to find the answers you need. With more than 140 commands, SPL gives you the power to ask any question of machine data. However, many users (both newbies and experienced users) find the language difficult to grasp and complex. This book takes you through the basics of SPL using plenty of hands-on examples and emphasizes the most impactful SPL commands (such as eval, stats, and timechart). You will understand the most efficient ways to query Splunk (such as learning the drawbacks of subsearches and join, and why it makes sense to use tstats). You will be introduced to lesser-known commands that can be very useful, such as using the command rex to extract fieldsand erex to generate regular expressions automatically. In addition, you will learn how to create basic visualizations (such as charts and tables) and use prescriptive guidance on search optimization. For those ready to take it to the next level, the author introduces advanced commands such as predict, kmeans, and cluster. What You Will Learn Use real-world scenarios (such as analyzing a web access log) to search, group, correlate, and create reports using SPL commands Enhance your search results using lookups and create new lookup tables using SPL commands Extract fields from your search results Compare data from multiple time frames in one chart (such as comparing your current day application performance to the average of the past 30 days) Analyze the performance of your search using Job Inspector and identify execution costs of various components of your search Who This Book Is For Application developers, architects, DevOps engineers, application support engineers, network operations center analysts, security operations center (SOC) analysts, and cyber security professionals who use Splunk to search and analyze their machine data
ASIN: 1484262751
VSKU: GBV.1484262751.A
Condition: Acceptable
Author/Artist:Subramanian, Karun
Binding: Paperback
Note: Any images shown are stock photographs and product may differ from what is shown.
Condition Notes: This book is in acceptable condition and may have highlighting and or writing throughout. The actual cover image may not match the stock photo, dust jacket may be damaged or missing. Book may show internal and or external wear on spine or cover and may be slightly skewed or have creased pages. This is a used book so codes may be invalid or accompanying media may be missing. May be an Ex library book with stickers and stamps.
Shipping

We currently ship retail orders within the United States. Orders are normally prepared for carrier handoff within 1–2 business days, excluding weekends and holidays. Carrier transit time is additional.

Available services and charges depend on order value, package weight, destination, and the method selected. Checkout shows the applicable options before payment; not every order qualifies for free shipping.

Read the shipping policy.

Returns

You may request a return within 30 calendar days after delivery. Contact us before sending a book back.

Customers pay change-of-mind return postage. For a wrong, damaged, or materially misdescribed item, we provide a prepaid return label or another resolution you accept. See the policy for eligibility, original shipping charges, and refund timing.
Read the returns and refund policy.

Practical Splunk Search Processing Language: A Guide for Mastering SPL Commands for Maximum Efficiency and Outcome